CYBER SECURITY
Powerful Tools To Protect Your Digital World
Network Sentinel
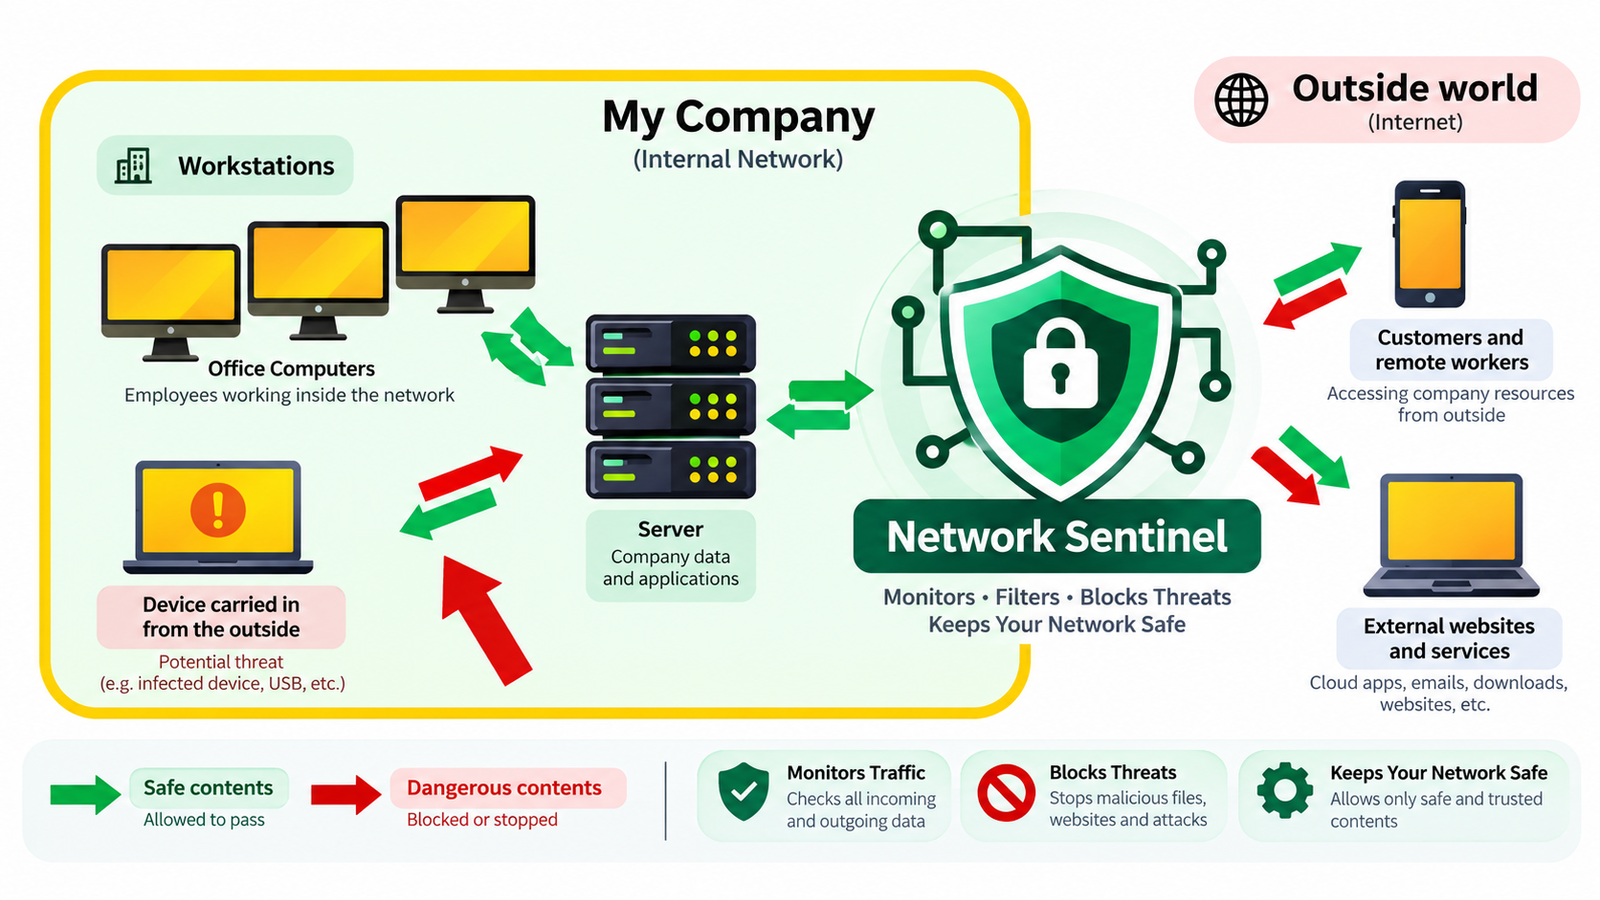
In today’s connected world, businesses and individuals rely on networks to communicate, work, store information, and access digital services. As the number of connected devices continues to grow, maintaining a secure network has become an important part of protecting digital operations.
Network Sentinel is a network security solution designed to help organizations strengthen their network environment, control access, protect information, and reduce exposure to common digital security risks.
Understanding Network Security
Network security refers to the technologies and practices used to protect computer networks and the information moving through them. It focuses on controlling access, identifying unusual activity, protecting communications, and maintaining the reliability of connected systems.
Network Sentinel brings these security principles together to provide a structured approach to network protection. It can help organizations establish stronger safeguards across devices, connections, users, and network resources.
The Role of Network Sentinel in Network Security
Protection Against Network Threats
Connected networks can encounter a variety of security risks, including unauthorized access, suspicious activity, malicious software, and other unwanted network behavior. Network Sentinel is designed to support network monitoring and protective controls that help organizations respond to potential security concerns.
Protecting Important Information
Business information often moves between computers, servers, applications, and connected devices. Strong network security helps keep this information protected while it is being transmitted and accessed.
Network Sentinel supports security measures intended to help restrict unauthorized access and provide greater control over sensitive network communications.
Maintaining Network Reliability
A dependable network requires more than connectivity. It also needs appropriate controls to help prevent unauthorized changes and unwanted activity.
Network Sentinel helps support a controlled network environment, allowing organizations to maintain better visibility over network activity and strengthen overall network integrity.
Key Components of Network Security
Firewall Protection
Firewalls help control network traffic according to defined security rules. They can separate trusted network resources from potentially unwanted connections and help restrict traffic that does not meet established requirements.
Network Sentinel incorporates network protection concepts that help organizations manage and control network communications more effectively.
Intrusion Detection and Prevention
Monitoring network activity can help identify unusual patterns and potential security events. Intrusion detection and prevention technologies analyze network behavior and can help organizations take appropriate action when suspicious activity is identified.
Network Sentinel is designed to support these types of network security controls for a more proactive security approach.
Encryption
Encryption converts information into a protected format so that it cannot be easily understood without the appropriate authorization or key.
Using encryption as part of a network security strategy can provide an additional layer of protection for information exchanged across connected systems.
Wireless Network Security
Wireless connections are now an essential part of many business environments. Properly configured wireless security can help prevent unauthorized users from accessing network resources.
Network Sentinel supports security practices designed to help organizations maintain better control over wireless network access and communications.
Access Control
Not every user or device should have unrestricted access to every network resource. Access control helps organizations determine who or what can connect to specific systems and services.
Network Sentinel can be used as part of an access-control strategy to help organizations establish appropriate authentication and authorization practices.
Virtual Private Networks (VPNs)
VPN technology provides a protected connection between a user and a network over an internet connection. It is commonly used when employees or other authorized users need to access network resources remotely.
Network Sentinel supports a broader network security strategy that can include secure remote connectivity and controlled access to organizational resources.
Why Network Security Matters
As organizations become increasingly dependent on connected technology, network protection needs to evolve alongside emerging security challenges. Regular monitoring, appropriate configuration, access management, security updates, and well-defined policies all contribute to a stronger security environment.
Network Sentinel provides a network security-focused approach for organizations looking to improve visibility, manage access, and strengthen the protection of their connected infrastructure.
A well-managed network can help businesses operate with greater confidence while keeping important systems and information better protected. With the right security controls in place, organizations can build a more resilient digital environment prepared to address changing network security requirements.
ThreatGrid
The internet connects us to information, services, and people around the world, but every online connection can also reveal information about your digital identity. Your IP address can provide clues about your approximate location and network, making online privacy an important consideration.
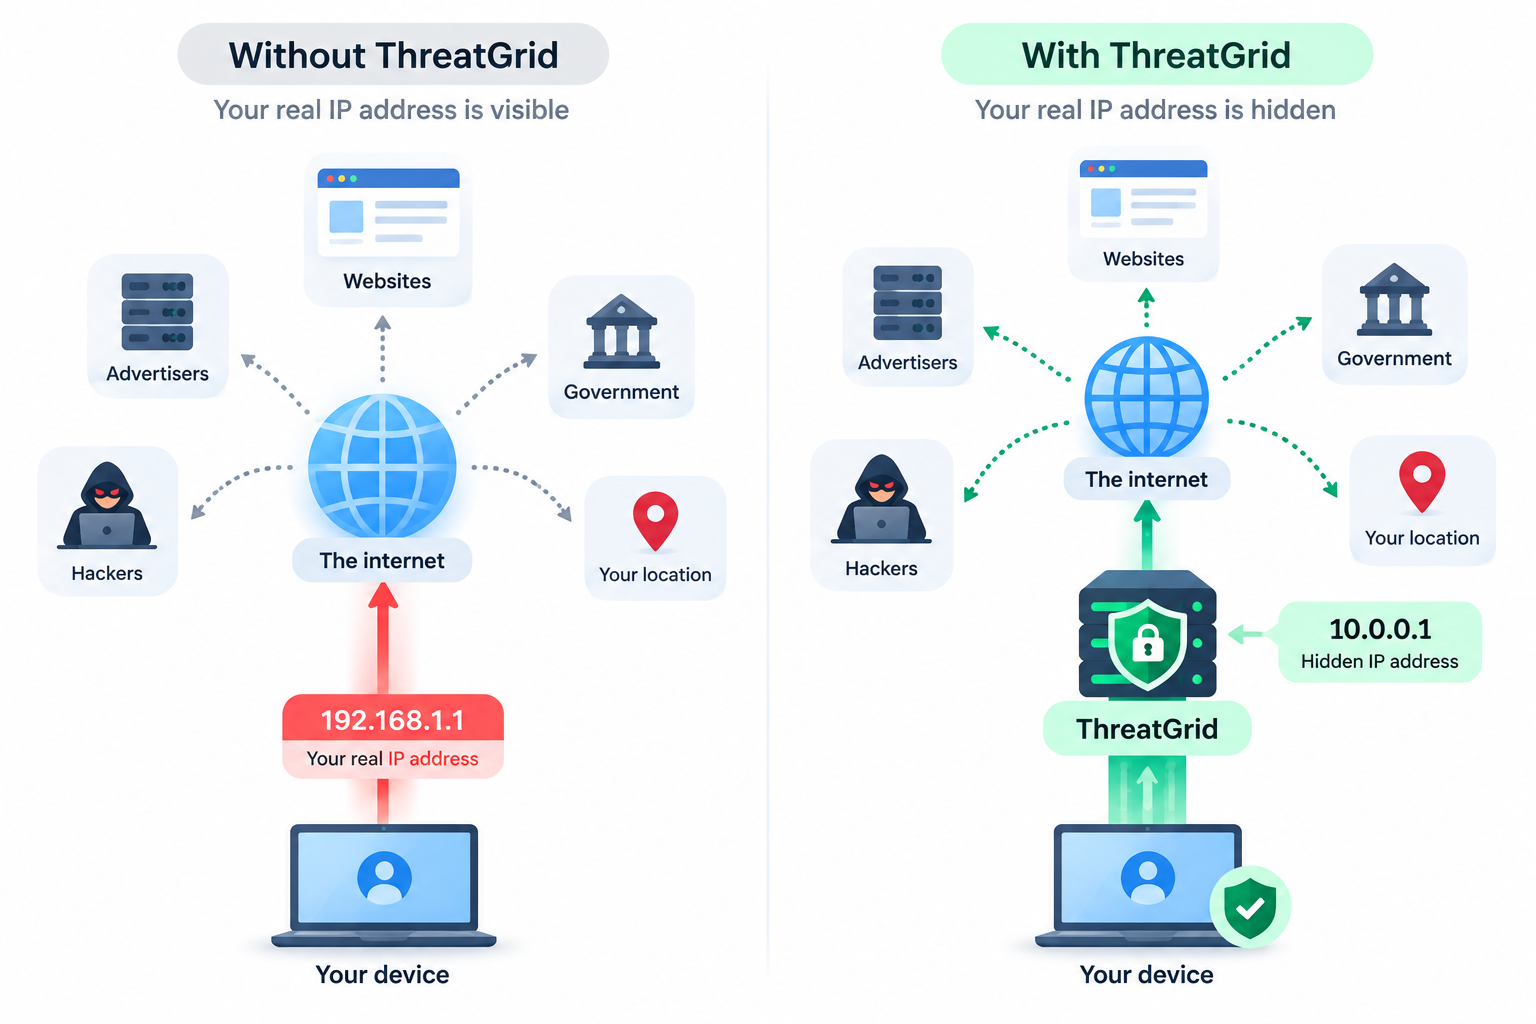
ThreatGrid is an IP Hider designed to help protect your online identity by masking your real IP address and routing your internet connection through a different network address. This creates an additional privacy layer between your device and the websites or online services you access.
What Is an IP Hider and How Does It Work?
An IP Hider is a privacy tool that helps conceal your device’s original IP address when you connect to the internet. Instead of directly exposing your real network address to websites and online services, your connection can be routed through an intermediary server.
ThreatGrid works by acting as a privacy layer between your device and the internet. When a connection is routed through ThreatGrid, the destination service sees the IP address associated with the intermediary connection rather than your original IP address.
This can help reduce the amount of network information directly exposed during everyday browsing. By placing an additional layer between your device and the destination, ThreatGrid can help provide a more private browsing experience.
Why Use ThreatGrid as an IP Hider?
Protecting your digital privacy involves more than simply keeping passwords secure. Your network information can also contribute to your online footprint. ThreatGrid provides several privacy-focused benefits for users who want greater control over how their internet connection is exposed.
Private and Anonymous Browsing
An IP Hider can make it more difficult for websites and online services to directly associate your activity with your original IP address.
ThreatGrid helps mask your IP address, adding a privacy layer while you browse the web. This can be particularly useful when you want to minimize the exposure of your network information during everyday online activities.
Access Content From Different Regions
Some websites and online services provide different content depending on a user’s geographic location.
ThreatGrid can help route your connection through available network locations, potentially allowing you to access services that are available in those regions. Availability and access can vary depending on the destination service and applicable local restrictions.
Additional Online Security
Using an IP Hider can provide an additional layer between your device and the public internet.
ThreatGrid is designed to help conceal your original IP address, reducing its direct exposure to websites and online services. Combined with other security practices, this can contribute to a stronger overall approach to online privacy.
Safer Browsing on Public Networks
Public Wi-Fi networks are convenient, but connecting through shared networks can create additional privacy and security concerns.
ThreatGrid can add a privacy layer by routing your connection through its network infrastructure. This can help reduce direct exposure of your original IP address while browsing from locations such as cafés, airports, hotels, or other public spaces.
However, an IP Hider should complement—not replace—basic security measures such as HTTPS, strong passwords, device updates, and multi-factor authentication.
Support for a More Private Internet Experience
Internet access can be subject to network-level restrictions, regional availability, and other limitations.
ThreatGrid gives users greater control over the IP address presented to online services, helping create a more flexible and privacy-conscious browsing experience. Always use such capabilities in accordance with applicable laws and the terms of the services you access.
Choosing ThreatGrid as Your IP Hider
Choosing an IP Hider requires more than simply looking at whether it can hide an IP address. Consider factors such as connection performance, available server locations, privacy features, encryption, reliability, compatibility, and ease of use.
ThreatGrid is designed around the goal of providing users with a practical privacy layer for their internet connections while helping them maintain greater control over their online network identity.
Protect Your Online Identity With ThreatGrid
Your IP address is an important part of your internet connection, and keeping it from being unnecessarily exposed can be an important part of a broader privacy strategy.
ThreatGrid provides an IP Hider solution that helps mask your original IP address and adds an intermediary layer between your device and the websites you visit.
Whether your priority is IP address privacy, private browsing, public Wi-Fi protection, or greater control over your online connection, ThreatGrid can be part of a broader approach to maintaining a more private digital experience.
SecureGate
As digital systems become increasingly connected, protecting networks from unauthorized access and cyber threats has become essential. Businesses, organizations, and individuals need reliable security controls to monitor network activity and prevent suspicious connections from reaching critical systems.
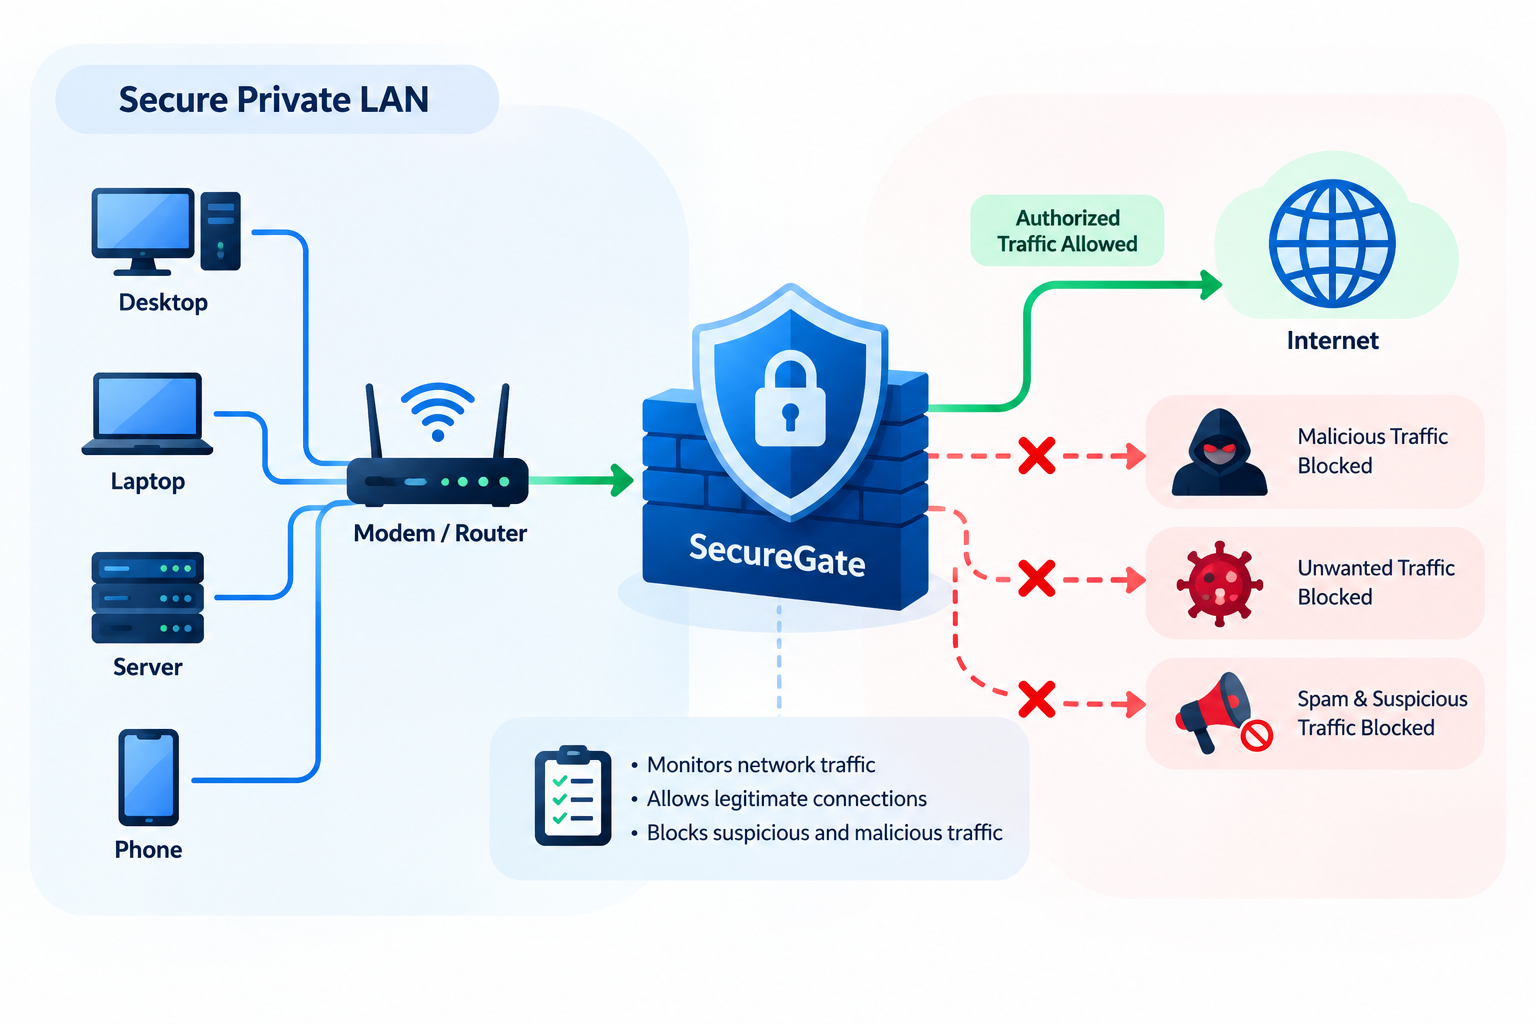
SecureGate is a firewall solution designed to act as a protective layer between trusted networks and potentially harmful external traffic. By inspecting network connections and applying security rules, SecureGate helps control which traffic can enter or leave a protected environment.
What Is a Firewall and How Does It Work?
A firewall is a network security system that controls incoming and outgoing traffic according to predefined security policies. It creates a boundary between a trusted network and external networks, helping prevent unauthorized connections from reaching protected devices and resources.
SecureGate monitors network traffic and evaluates connection requests against configured security rules. Depending on the defined policies, traffic can be permitted, restricted, or blocked.
This approach helps organizations maintain greater visibility and control over network communications while reducing exposure to potentially harmful traffic.
SecureGate sits between external traffic and the protected environment, examining network activity before allowing approved connections to continue.
Key Benefits of SecureGate Firewall
Blocking Unauthorized Network Access
One of the primary functions of a firewall is controlling who and what can communicate with a protected network.
SecureGate evaluates incoming and outgoing traffic based on established security policies. Suspicious or unauthorized connection attempts can be restricted, helping reduce the risk of unwanted access to sensitive systems and resources.
Intelligent Traffic Filtering
Modern networks handle large volumes of data every second, making effective traffic filtering an important part of network security.
SecureGate uses configurable rules to distinguish between permitted and restricted traffic. Security policies can help control connections based on factors such as network addresses, ports, protocols, and other traffic characteristics.
This provides administrators with greater control over how data moves across the network.
Adaptive Network Protection
Cyber threats continue to change, which means network security cannot rely solely on static defenses.
SecureGate is designed to support flexible security policies that can be adjusted as network requirements and threat conditions change. Administrators can refine firewall rules and access controls to respond to new security requirements and emerging risks.
Network Segmentation and Access Control
Dividing a network into separate segments can help limit unnecessary communication between systems and reduce the potential impact of a security incident.
SecureGate can support network segmentation and access-control strategies by controlling traffic between different network zones. This allows organizations to establish more focused security boundaries around critical systems, applications, and resources.
Allowing Trusted Network Traffic
A firewall is not simply designed to block everything. Legitimate applications and users still need reliable access to authorized services.
SecureGate allows administrators to define security policies that permit trusted traffic while restricting connections that do not meet established requirements. This helps maintain the balance between network protection, accessibility, and operational continuity.
Why Choose SecureGate Firewall?
A strong firewall strategy should provide more than basic traffic blocking. It should help organizations establish clear network boundaries, control communication, and maintain visibility over network activity.
SecureGate provides a centralized security layer for managing network traffic and enforcing access policies. Whether protecting business infrastructure, internal systems, applications, or connected devices, a properly configured firewall can play an important role in a broader cybersecurity strategy.
Strengthen Your Network Security With SecureGate
As networks become more distributed and cyber threats continue to evolve, controlling network traffic is an important part of maintaining a secure digital environment.
SecureGate Firewall helps protect network boundaries by inspecting traffic, enforcing access rules, restricting unauthorized connections, and supporting controlled communication between network segments.
With the right security policies and configuration, SecureGate can serve as an important component of a defense-in-depth cybersecurity strategy, helping organizations protect their infrastructure while keeping legitimate network traffic moving efficiently
RanShield
Ransomware has become one of the most disruptive cybersecurity threats facing individuals and organizations today. A single malicious file or compromised account can potentially lead to encrypted data, operational downtime, and significant recovery challenges.
RanShield is an anti-ransomware security solution designed to help detect suspicious activity, identify ransomware-like behavior, and prevent malicious processes from causing widespread damage. By adding an additional layer of protection to your security environment, RanShield helps safeguard important files and digital resources against evolving ransomware threats.
Understanding the Ransomware Threat
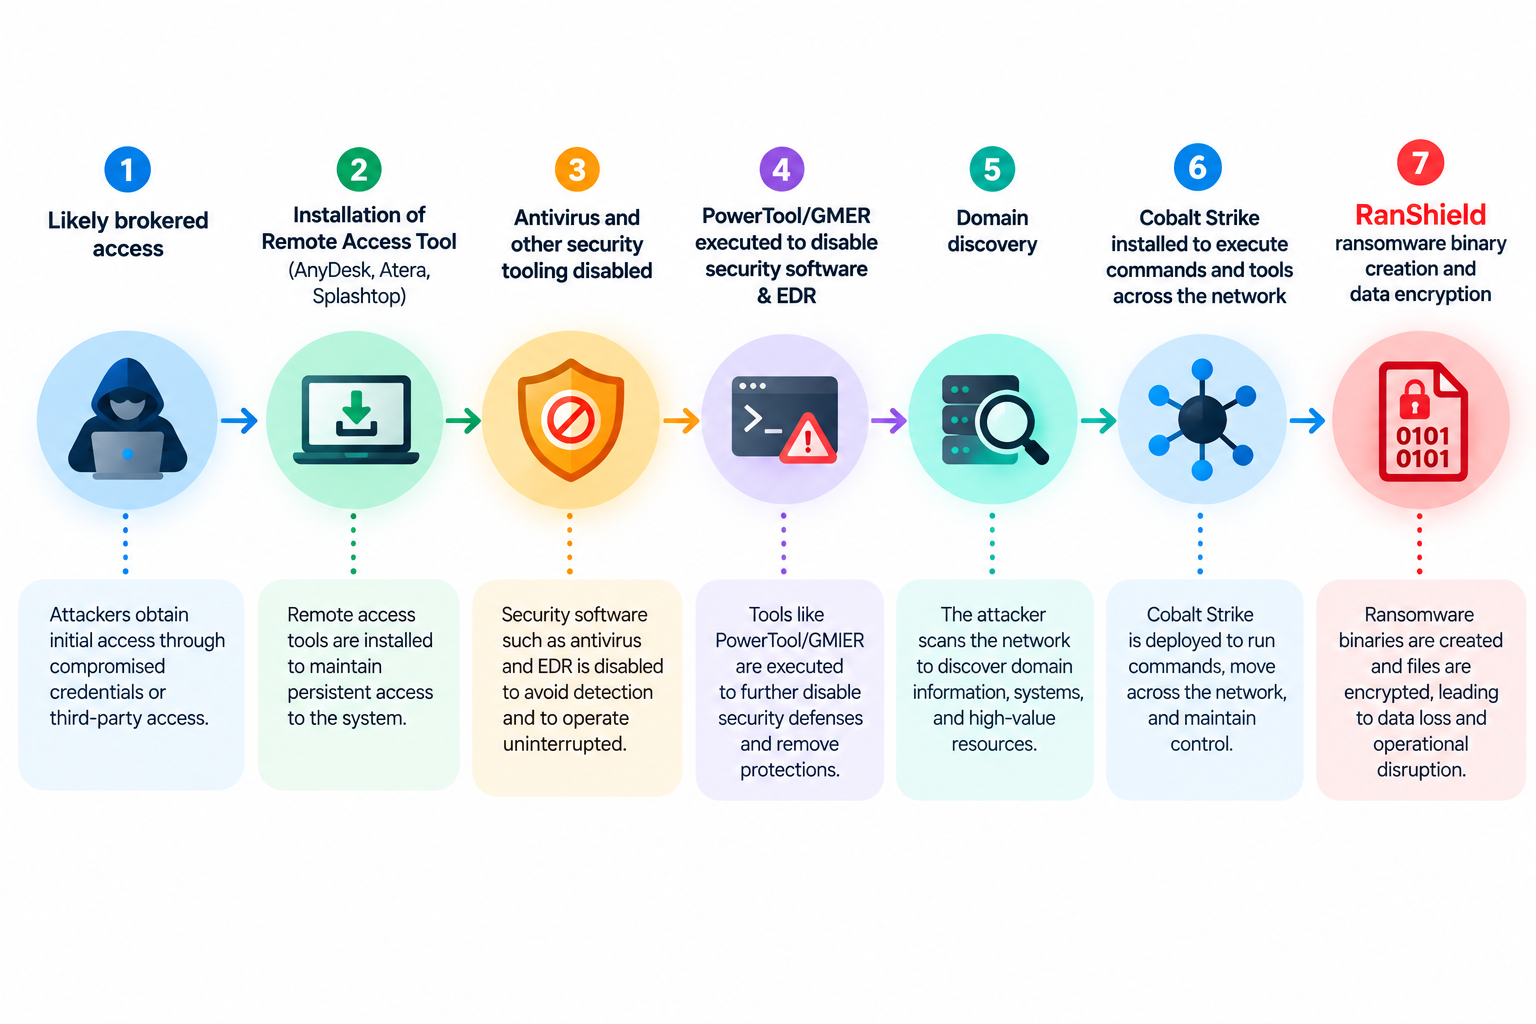
Ransomware is a type of malware that attempts to deny access to files or systems, commonly by encrypting data and demanding payment from the victim.
A ransomware incident can begin through various attack vectors, including malicious email attachments, compromised websites, stolen credentials, vulnerable applications, or unauthorized remote access.
Once ransomware gains a foothold, attackers may attempt to move through a network, disable security controls, access sensitive information, and encrypt critical files.
This makes early detection and behavioral protection important components of a modern cybersecurity strategy.
Why Anti-Ransomware Protection Matters
Traditional security tools may rely heavily on known malware signatures. Modern ransomware campaigns, however, can change rapidly and may use new or modified techniques to evade conventional detection.
RanShield takes a proactive approach by focusing on suspicious behavior and ransomware-related activity. Instead of relying only on previously identified threats, anti-ransomware protection can monitor activity that may indicate an attempted attack.
This additional security layer can help organizations respond to ransomware activity before it develops into a larger incident.
Proactive Ransomware Defense
Waiting until files have already been encrypted can make ransomware incidents significantly more difficult to contain.
RanShield is designed to identify suspicious file and system activity that may be associated with ransomware behavior. Detecting unusual activity earlier can help security teams investigate potential threats and take appropriate action before extensive damage occurs.
A proactive defense strategy can be particularly valuable for environments containing business-critical documents, customer information, databases, and other important digital assets.
Real-Time Threat Monitoring
Ransomware attacks can develop quickly, making continuous monitoring an important part of endpoint and network security.
RanShield provides a security layer designed to monitor for potentially malicious activity in real time. By observing changes in system and file behavior, the solution can help identify activity that may require investigation.
Continuous protection helps reduce the window between the beginning of a suspicious event and its detection.
Protecting Important Files and Data
Files are often among the most valuable assets targeted during ransomware attacks.
RanShield is designed to help protect important data from suspicious encryption and other ransomware-related activity. By adding anti-ransomware controls to your security strategy, organizations can strengthen their defenses around critical files and digital resources.
For stronger protection, anti-ransomware technology should also be combined with regular backups, access controls, software updates, and employee security awareness.
Detecting Suspicious Ransomware Behavior
Modern ransomware can use different techniques to compromise systems, making behavioral analysis an important security capability.
RanShield focuses on identifying activity that may indicate ransomware execution or unauthorized file manipulation. Suspicious processes and abnormal changes can serve as indicators that additional investigation or security action may be required.
This behavior-focused approach can complement traditional antivirus and endpoint security technologies.
Helping Reduce the Impact of Ransomware Attacks
No single cybersecurity product can guarantee complete protection from every ransomware attack. However, layered security can significantly improve an organization’s ability to prevent, detect, and respond to threats.
RanShield adds an anti-ransomware layer that can work alongside other security measures to help reduce potential damage and improve overall resilience.
Build a Stronger Ransomware Defense With RanShield
Ransomware continues to evolve, making reactive security alone insufficient for many modern environments. Organizations need security strategies that combine prevention, detection, monitoring, response, and recovery.
RanShield Anti-Ransomware is designed to help strengthen this approach by monitoring suspicious behavior and providing an additional layer of protection against ransomware activity.
Whether you’re protecting business documents, employee endpoints, sensitive information, or critical digital infrastructure, RanShield can form part of a broader ransomware protection and cybersecurity strategy.
Choose Proactive Protection With RanShield
A strong defense against ransomware begins before an attack becomes a major incident.
With RanShield, organizations can add dedicated anti-ransomware protection to their cybersecurity architecture, helping identify suspicious activity and protect valuable digital assets.
Combine RanShield with secure backups, strong authentication, network segmentation, endpoint protection, patch management, and security awareness to create a more resilient defense against today’s evolving ransomware landscape.
VaultCore
Digital information moves constantly between devices, applications, servers, and cloud environments. From personal credentials and business documents to financial information and private communications, sensitive data needs protection wherever it is stored or transmitted.
VaultCore is encryption software designed to help protect sensitive information by transforming readable data into an encoded format that cannot be easily understood without the appropriate decryption key. By adding encryption to your security strategy, VaultCore helps strengthen data confidentiality and reduce the risk of unauthorized access.
What Is Encryption?
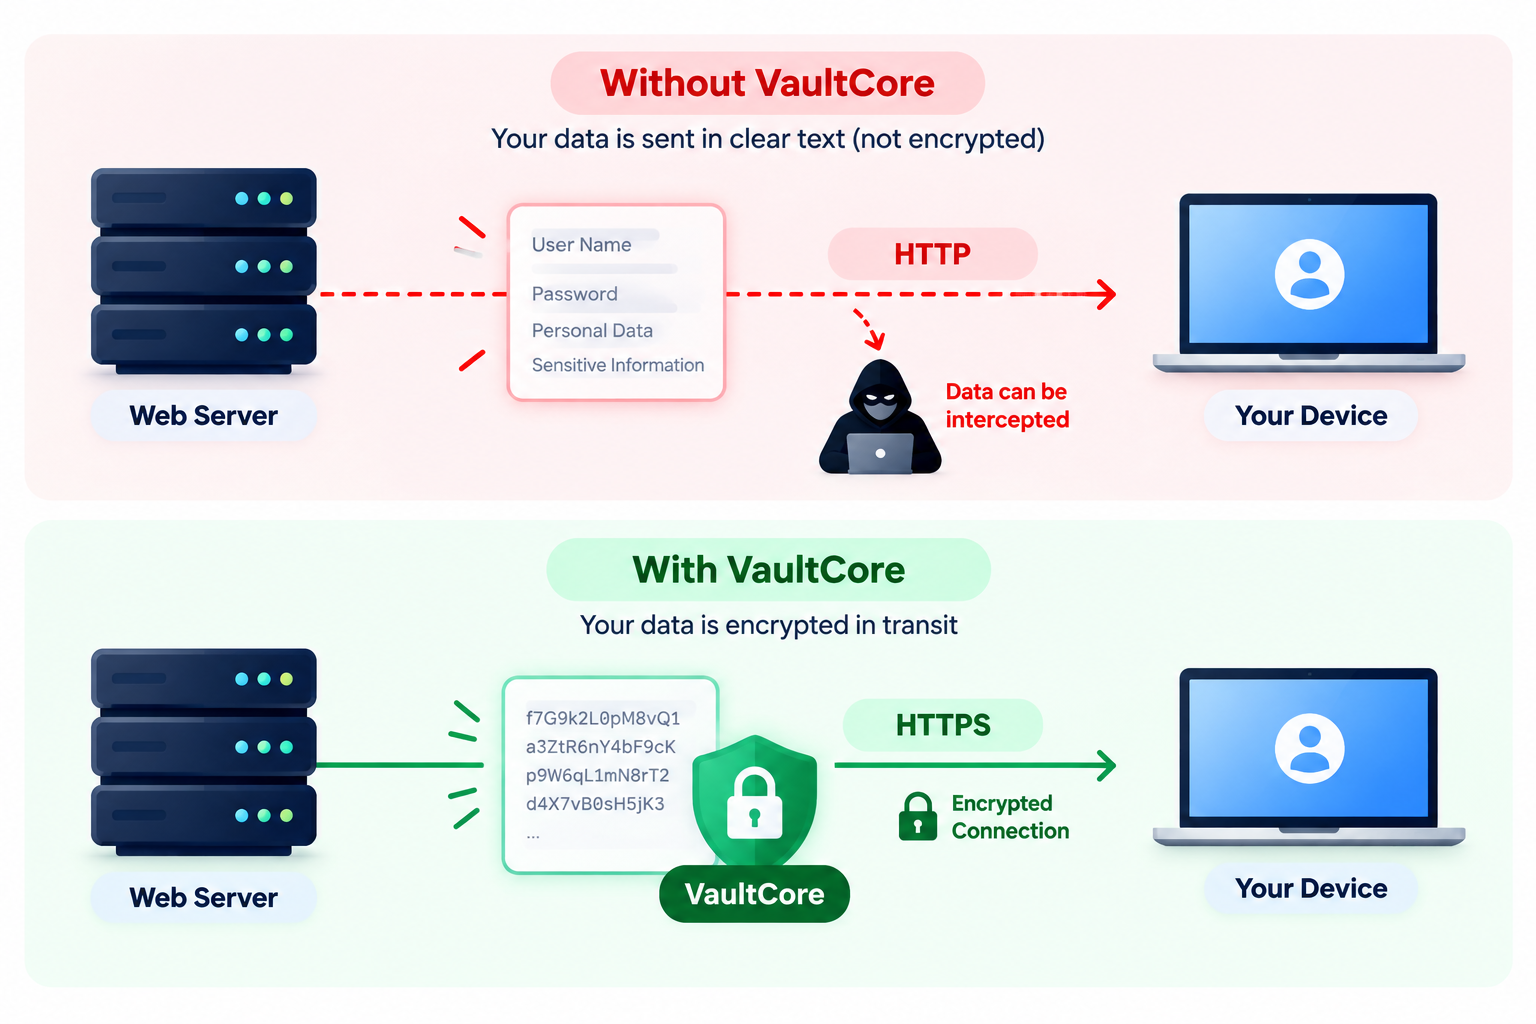
Encryption is a security process that converts readable information, known as plaintext, into an encoded form called ciphertext.
A cryptographic algorithm uses an encryption key to transform the original information. The encrypted data can then be decrypted by an authorized party using the appropriate key or credentials.
When the encrypted information needs to be accessed, the appropriate decryption process converts it back into its original form.
This makes encryption an important technology for protecting sensitive information from unauthorized users.
How VaultCore Encryption Software Helps Protect Data
Encryption can protect information in different environments, including data being transmitted across networks and information stored on devices or servers.
VaultCore can serve as an additional security layer for organizations that need to protect confidential digital assets and maintain control over access to sensitive information.
Protecting Data in Transit
Information frequently travels between computers, applications, servers, and online services. Without appropriate protection, sensitive information may be exposed during transmission.
Encryption helps secure data while it moves between trusted endpoints by converting information into an encoded format.
VaultCore can be incorporated into a broader data-security strategy to help protect sensitive information as it moves through digital environments.
Securing Stored Data
Protecting information doesn’t end when data reaches its destination. Stored files and databases can also become targets for unauthorized access.
Encryption can help protect data stored on computers, servers, storage devices, and other digital systems. If encrypted information is accessed without the appropriate key or authorization, the underlying content remains protected rather than immediately appearing in readable form.
VaultCore is designed to support a security-first approach to protecting sensitive stored information.
Strengthening Data Privacy
Organizations manage large amounts of confidential information, including customer records, financial documents, credentials, intellectual property, and internal communications.
VaultCore encryption software can help organizations add stronger confidentiality controls around sensitive information. Encryption can reduce the risk associated with unauthorized access by ensuring that protected data is not readily readable without the required authorization.
Encryption for Secure Digital Communications
Modern businesses rely heavily on digital communication. Emails, file transfers, collaboration platforms, and other communication channels can contain sensitive information.
Encryption helps protect the confidentiality of digital communications by encoding information so that only authorized parties with the necessary decryption capability can access the original content.
VaultCore can form part of a broader secure-communication strategy alongside authentication, access controls, and other cybersecurity measures.
Encryption and Cybersecurity
Cyber threats can target data at almost every stage of its lifecycle. Attackers may attempt to steal information through compromised accounts, malware, vulnerable systems, or unauthorized access.
Encryption provides an important defensive layer by protecting the actual contents of sensitive information.
Even when encrypted data is obtained by an unauthorized party, strong encryption can make the information significantly more difficult to interpret without the required cryptographic key.
However, encryption works best as part of a layered cybersecurity strategy that also includes strong authentication, access management, secure backups, endpoint protection, network security, and regular software updates.
Secure Data With VaultCore
Data is one of the most valuable assets in today’s connected world. Protecting that data requires security measures that work across storage, communication, and everyday digital operations.
VaultCore provides encryption software designed to help organizations protect sensitive information through cryptographic data protection. By converting readable information into protected ciphertext, VaultCore can help strengthen confidentiality and reduce unnecessary exposure of valuable digital assets.
Whether you’re protecting business files, confidential documents, customer information, credentials, or other sensitive data, encryption can be an essential component of a modern data-protection strategy.
Why Choose VaultCore Encryption Software?
Effective encryption is about more than simply encoding information. Organizations should also consider factors such as encryption strength, key management, access controls, compatibility, performance, scalability, and ease of administration.
VaultCore is designed to provide a security-focused approach to protecting digital information while helping organizations build stronger data confidentiality practices.
Strengthen Data Security With VaultCore
As the volume of digital information continues to grow, protecting sensitive data has become a fundamental part of cybersecurity.
VaultCore Encryption Software helps provide an additional layer of protection by encrypting sensitive information and limiting its readability to authorized users.
When combined with strong security policies and responsible key management, VaultCore can help organizations create a more resilient approach to data privacy, confidentiality, and information security.
CleanBox
Email and digital messaging have become essential for everyday communication, but unwanted messages can quickly overwhelm inboxes and create security risks. Spam can range from harmless promotional messages to phishing attempts, malicious links, fraudulent emails, and other unwanted content.
CleanBox is an anti-spam solution designed to help identify, filter, and manage unwanted messages before they reach users’ inboxes. By adding an intelligent filtering layer to email security, CleanBox helps organizations maintain cleaner inboxes while reducing exposure to potentially harmful messages.
What Is Spam and Why Is It a Security Concern?
Spam refers to unsolicited or unwanted digital messages, most commonly delivered through email. While some spam is simply inconvenient, malicious campaigns can be used to distribute phishing links, malware, fraudulent offers, and social-engineering attacks.
A seemingly ordinary email can potentially direct users to a fake website, request confidential information, or contain a harmful attachment.
For this reason, effective spam filtering is not only about keeping inboxes organized—it can also contribute to a broader cybersecurity strategy.
How CleanBox Anti-Spam Protection Works
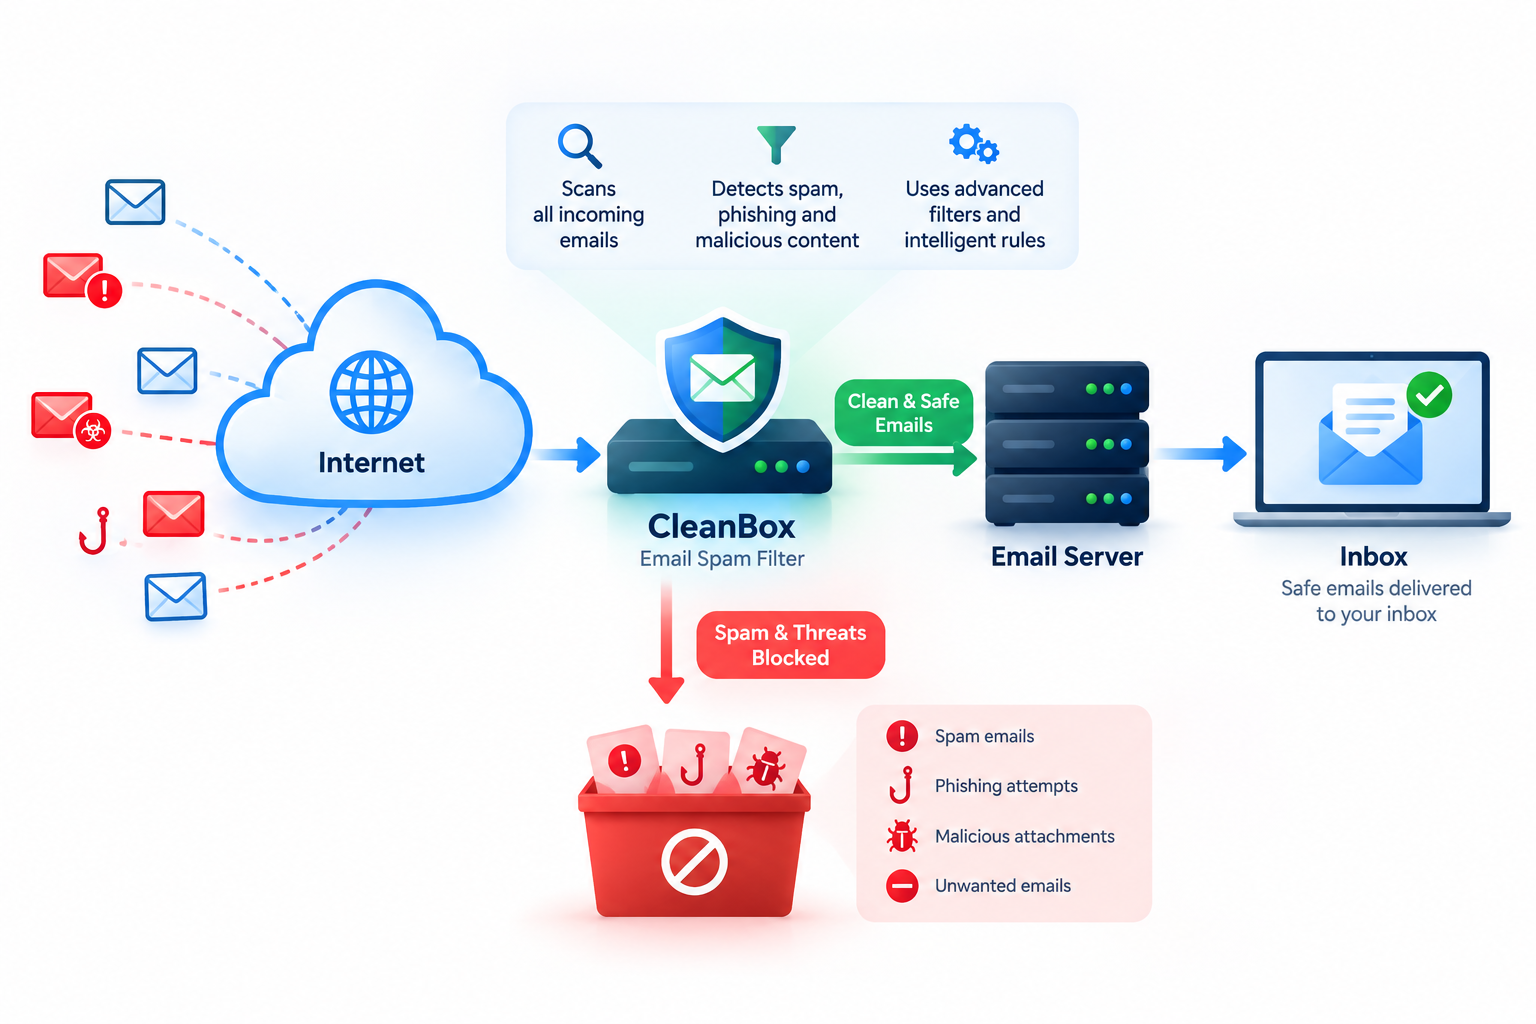
An anti-spam solution analyzes incoming messages and applies filtering policies to determine whether an email should be delivered, flagged, quarantined, or rejected.
CleanBox can evaluate different characteristics of incoming messages to help distinguish legitimate communication from unwanted or potentially suspicious content.
Key Features and Benefits of CleanBox
Intelligent Spam Filtering
Modern inboxes can receive large volumes of email, making manual spam management inefficient.
CleanBox is designed to analyze incoming messages and apply filtering rules to identify unwanted communication. This helps reduce inbox clutter while allowing legitimate messages to reach their intended recipients.
Effective filtering can consider multiple indicators rather than relying on a single characteristic of an email.
Protection Against Phishing Emails
Spam campaigns are frequently used as a delivery mechanism for phishing attacks.
Phishing emails may attempt to imitate trusted organizations, encourage users to click malicious links, or request sensitive information such as passwords and financial details.
CleanBox can form an important part of an email security strategy by helping identify and filter suspicious messages before they reach users.
Sender and Email Authentication
Email authentication technologies can help organizations verify whether messages are being sent from authorized sources.
Standards such as SPF, DKIM, and DMARC can work alongside anti-spam solutions to improve email trust and reduce risks associated with spoofed or fraudulent messages.
CleanBox can complement these authentication mechanisms as part of a layered approach to email security.
Adaptive Spam Detection
Spam techniques continue to change as attackers experiment with new message formats, domains, sender identities, and delivery methods.
An effective anti-spam solution needs to adapt to changing patterns rather than relying exclusively on fixed rules.
CleanBox is designed to support dynamic filtering and detection strategies that can help identify emerging forms of unwanted or suspicious email activity.
Reduce Inbox Clutter
A constantly overloaded inbox can make it difficult for users to identify important communications.
By filtering unwanted messages before they reach the primary inbox, CleanBox can help create a more organized email environment.
Reducing unnecessary messages also allows employees to spend less time manually sorting through unwanted communication.
CleanBox and Email Security
Spam filtering is an important component of a broader email-security strategy, but it should not operate alone.
Organizations can strengthen their defenses by combining CleanBox with email authentication, endpoint security, secure passwords, multi-factor authentication, employee awareness training, and regular security updates.
This layered approach can help reduce the opportunities attackers have to use email as an entry point for phishing, malware, and other cyber threats.
User Awareness Still Matters
Technology can help filter suspicious messages, but users remain an important part of email security.
Employees should be encouraged to verify unexpected requests, avoid opening suspicious attachments, inspect unfamiliar links, and report questionable messages.
CleanBox can reduce the volume of unwanted and potentially suspicious emails reaching users, while security awareness helps users make safer decisions when legitimate messages do arrive.
Create a Cleaner and Safer Inbox With CleanBox
Unwanted email is more than an inconvenience. Spam campaigns can contribute to phishing, fraud, malware distribution, and other cybersecurity risks.
CleanBox Anti-Spam is designed to help organizations filter unwanted messages, identify suspicious email activity, and maintain a cleaner communication environment.
By combining intelligent filtering with email authentication, security policies, and user awareness, CleanBox can become an important layer in a modern email security and anti-spam strategy.
Strengthen Email Protection With CleanBox
As email threats continue to evolve, organizations need practical tools to control unwanted communication without disrupting legitimate business messages.
CleanBox provides an anti-spam security layer designed to help filter unwanted email and reduce exposure to potentially harmful messages.
Whether you’re protecting a business inbox, organizational email system, or large-scale communication environment, CleanBox can help create a cleaner, more controlled, and security-focused email experience.
SpyNox
Cyber threats are becoming increasingly sophisticated, and spyware remains a significant concern for individuals and organizations. Unlike threats that are immediately visible, spyware can operate quietly in the background, attempting to collect sensitive information without the user’s knowledge.
SpyNox is an anti-spyware security solution designed to help detect, block, and remove spyware and other suspicious software before they can compromise sensitive information. By combining multiple detection approaches with continuous monitoring, SpyNox adds an important layer of protection to your cybersecurity environment.
What Is Spyware?
Spyware is a type of unwanted or malicious software designed to monitor activity or collect information from a device without appropriate user consent.
Depending on its capabilities, spyware may attempt to capture browsing activity, credentials, personal information, application data, or other sensitive details. Some spyware can operate quietly for extended periods, making detection particularly challenging.
Spyware can enter a system through malicious downloads, compromised websites, unsafe attachments, bundled software, or other attack methods.
Why Anti-Spyware Protection Matters
Traditional security measures may not always identify every form of unwanted surveillance software, particularly when threats are modified or designed to avoid conventional detection.
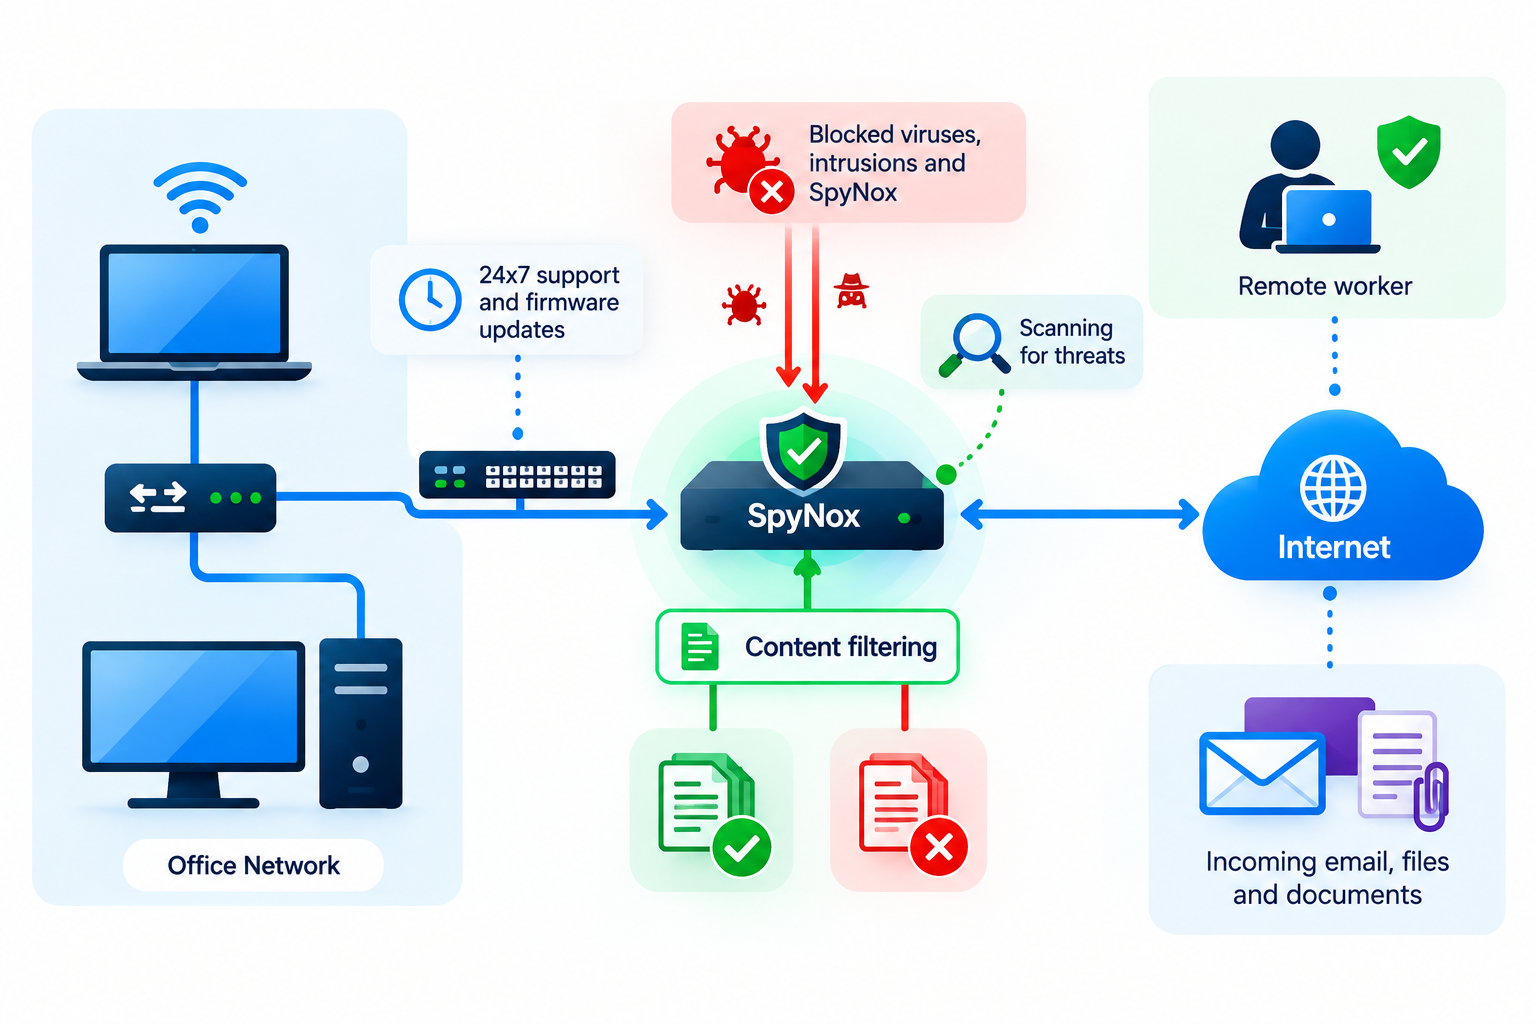
SpyNox provides an additional security layer focused on identifying suspicious software and activity associated with spyware. By combining real-time monitoring with multiple detection techniques, it can help organizations strengthen their defenses against covert threats.
Real-Time Spyware Monitoring
Spyware can cause significant problems when it remains undetected for long periods.
SpyNox is designed to continuously monitor system activity for suspicious behavior that may indicate spyware or other potentially unwanted software.
Real-time monitoring can help identify unusual activity earlier, allowing security teams or users to investigate potential threats before they become a larger security issue.
Behavioral and Heuristic Detection
Not every spyware threat has a known signature.
SpyNox can use behavioral and heuristic analysis to examine suspicious software activity and identify patterns that may indicate malicious intent. This approach can help detect potentially harmful programs even when they do not exactly match previously identified threat signatures.
Behavior-based detection provides an additional layer of protection against new or modified spyware variants.
Signature-Based Spyware Detection
Known spyware threats can often be identified through recognized malware signatures and threat indicators.
SpyNox can complement behavioral analysis with signature-based detection to help identify known spyware variants. Keeping detection intelligence and security definitions current can improve the ability to recognize established threats.
Using both known-threat detection and behavior-based analysis creates a more comprehensive anti-spyware strategy.
Detecting Suspicious Applications
Spyware can sometimes disguise itself as legitimate software or operate through processes that appear harmless.
SpyNox is designed to examine potentially suspicious applications and system activity for indicators associated with spyware.
When potentially unwanted or malicious behavior is detected, appropriate security actions can help isolate or remove the threat, depending on the configured security policies.
Protect Sensitive Information From Spyware
Spyware can target information that is valuable to both individuals and organizations.
This may include:
-Login credentials
-Personal information
-Business documents
-Browsing activity
-Application data
-Confidential communications
Other sensitive digital information
By detecting suspicious software and monitoring potentially harmful behavior, SpyNox Anti-Spyware can help reduce the opportunity for covert software to access sensitive resources.
A Layered Approach to Anti-Spyware Security
No single security technology can eliminate every cybersecurity risk. Anti-spyware protection works most effectively when combined with other security controls.
SpyNox can complement technologies such as firewalls, antivirus protection, endpoint security, access controls, secure authentication, software updates, and security awareness training.
This layered approach helps organizations address threats from multiple directions rather than depending on a single security mechanism.
Proactive Protection Against Emerging Threats
Cyber threats constantly evolve, and spyware developers can modify their techniques to avoid detection.
SpyNox is designed to support a proactive security approach by combining threat detection methods and continuous system monitoring. This can help improve visibility into suspicious activity and provide an additional defense against emerging spyware threats.
Help Keep Devices More Secure
A compromised device can potentially expose both personal and organizational information.
By providing dedicated anti-spyware capabilities, SpyNox can help identify suspicious software and reduce the risk associated with covert monitoring activity.
For stronger protection, users should also maintain updated operating systems and applications, avoid untrusted downloads, use strong authentication, and follow established cybersecurity practices.
Strengthen Your Security With SpyNox
Spyware can be difficult to identify because it is often designed to remain unnoticed. Detecting suspicious activity early can therefore be an important part of protecting devices and sensitive information.
SpyNox Anti-Spyware provides a dedicated security layer designed to detect and help address spyware and suspicious software using real-time monitoring, behavioral analysis, heuristic detection, and signature-based techniques.
Whether you’re protecting individual devices, business endpoints, or a broader digital environment, SpyNox can form part of a comprehensive endpoint and cybersecurity protection strategy.
Choose Proactive Anti-Spyware Protection With SpyNox
Modern cybersecurity requires continuous attention to threats that can operate quietly in the background.
SpyNox helps strengthen your security posture by providing dedicated anti-spyware protection designed to identify suspicious software and activity before they can potentially compromise sensitive information.
Combined with strong security practices and layered protection, SpyNox can help create a more secure and resilient digital environment.
IronClad Defense Systems
As organizations become increasingly dependent on digital systems, the cybersecurity landscape continues to grow more complex. Connected devices, cloud platforms, applications, and remote work environments create more opportunities for cyber threats to emerge.
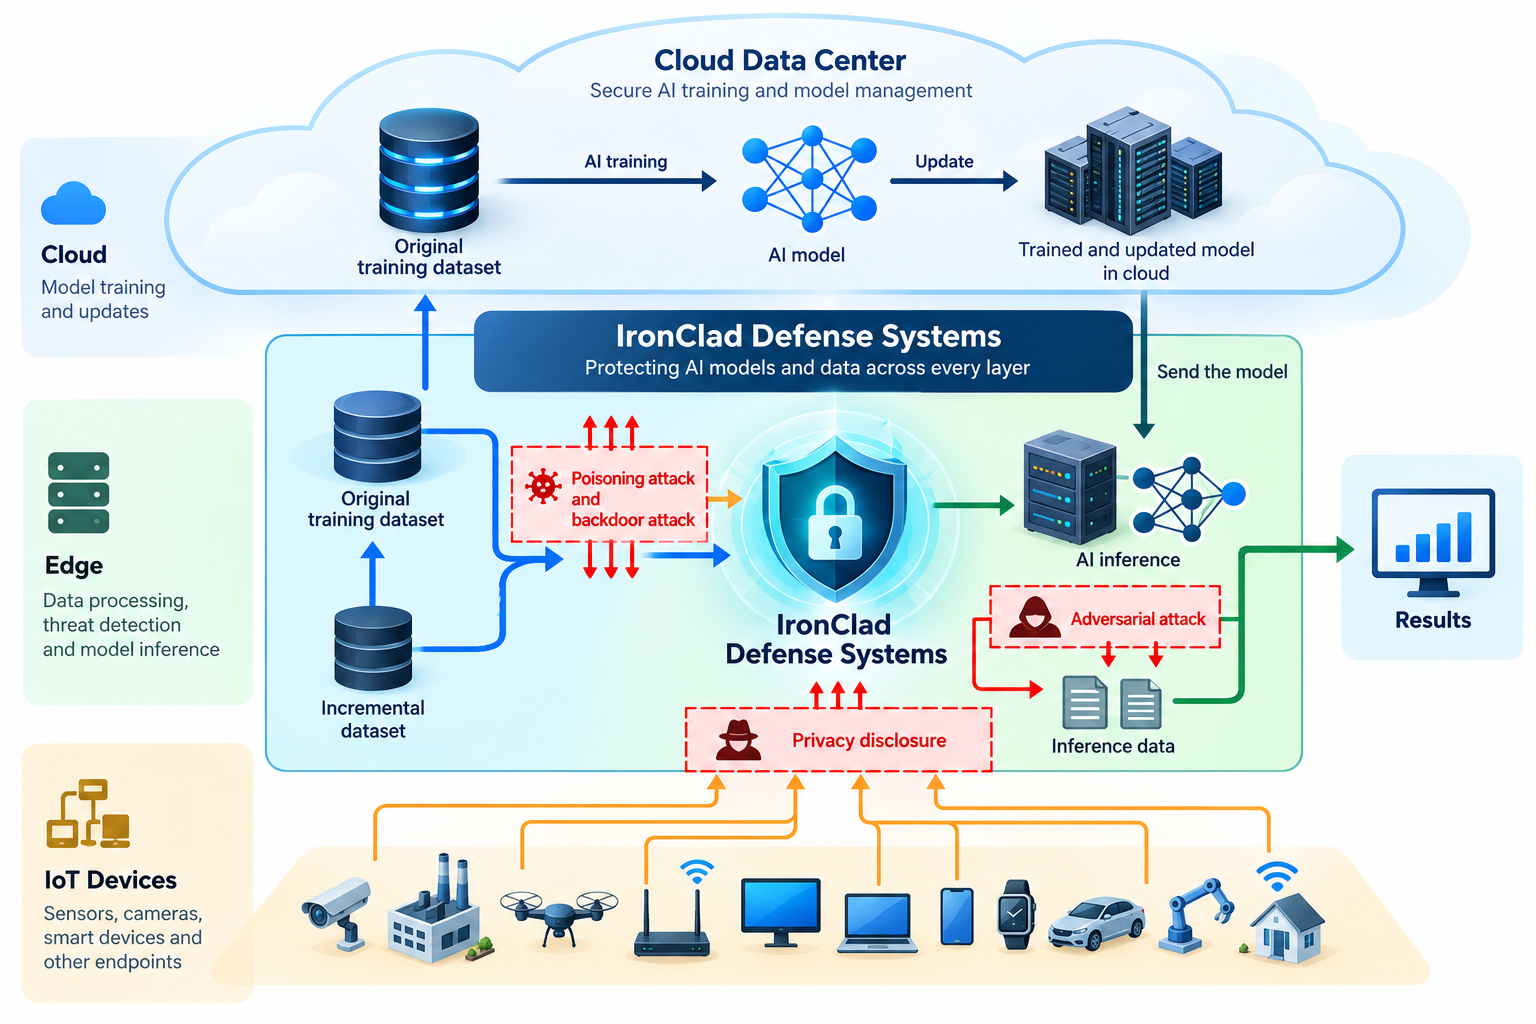
IronClad Defense Systems is an AI security solution designed to help organizations strengthen their cybersecurity posture through intelligent threat analysis, behavioral monitoring, and adaptive security capabilities. By using artificial intelligence and machine learning technologies, IronClad Defense Systems can help identify unusual activity and support faster responses to potential threats.
The Growing Challenge of Modern Cyber Threats
Cyberattacks are no longer limited to simple, easily recognizable patterns. Attackers continuously develop new techniques to exploit vulnerabilities, compromise accounts, manipulate users, and gain unauthorized access to digital environments.
Traditional security tools remain important, but increasingly complex threats require security systems capable of analyzing large volumes of information and identifying patterns that may otherwise be difficult to detect.
This is where AI-powered cybersecurity can provide an additional layer of intelligence.
How AI Security Works
AI security uses technologies such as machine learning, behavioral analytics, automated detection, and data analysis to identify potentially suspicious activity.
Rather than depending entirely on manually defined rules, an AI security platform can analyze activity across an environment and identify deviations from expected behavior.
IronClad Defense Systems is designed to support this approach by helping security teams identify potential anomalies and respond to changing threat conditions.
This intelligent approach can help organizations improve visibility across their digital environments and strengthen their ability to respond to emerging threats.
Key Benefits of IronClad Defense Systems AI Security
Proactive Threat Detection
Traditional security approaches may focus heavily on identifying threats after they have already been recognized.
AI-powered security can take a more proactive approach by analyzing patterns, relationships, and unusual behavior across large volumes of security data.
IronClad Defense Systems is designed to help identify potential indicators of compromise and suspicious activity, allowing security teams to investigate threats earlier and take appropriate action.
Machine Learning for Adaptive Security
Cyber threats continuously evolve, making static security controls less effective against certain emerging attack techniques.
Machine learning can help security systems recognize patterns and adapt their detection capabilities as new information becomes available.
IronClad Defense Systems uses an AI-focused security approach to support more adaptive threat detection and help organizations respond to changing cybersecurity conditions.
Intelligent Endpoint Protection
Computers, mobile devices, servers, and connected devices can all become potential entry points for cyberattacks.
IronClad Defense Systems can help strengthen endpoint security by analyzing device behavior and identifying activity that differs from established patterns.
Detecting unusual processes, access attempts, or system behavior can provide valuable signals for security teams investigating potential threats.
Identifying Suspicious Insider Activity
Not every security incident originates from outside an organization. Compromised accounts, accidental actions, or malicious insiders can also create security risks.
Behavioral analytics can help identify activity that deviates from a user’s normal patterns.
IronClad Defense Systems can support organizations in detecting unusual user behavior and identifying potential indicators of insider-related security incidents, helping security teams investigate activity before it develops into a larger problem.
Adaptive Access and Authentication
Authentication is a fundamental component of cybersecurity, but simply verifying a username and password may not always provide enough context.
AI-assisted security can analyze additional factors such as user behavior, access patterns, device information, and other contextual signals.
IronClad Defense Systems can support adaptive security strategies that help organizations evaluate access activity more intelligently and identify potentially abnormal authentication behavior.
AI Security for a Changing Threat Landscape
Cybersecurity environments generate enormous amounts of information every day. Security logs, endpoint activity, authentication events, network connections, and application behavior can all provide useful signals.
AI can help process and analyze this information at scale, allowing security teams to focus on meaningful anomalies instead of manually reviewing every event.
IronClad Defense Systems is designed to complement existing cybersecurity technologies by adding an intelligent analysis layer to the security ecosystem.
Strengthening a Layered Cybersecurity Strategy
AI security should not operate as a replacement for every other security control. The strongest cybersecurity strategies typically combine multiple layers of protection.
IronClad Defense Systems can complement technologies such as:
– Firewalls
– Endpoint security
– Anti-ransomware protection
– Anti-spyware solutions
– Identity and access management
– Encryption
– Secure authentication
– Network monitoring
– Security awareness programs
Together, these technologies can create a more comprehensive defense against modern cyber threats.
Why Choose IronClad Defense Systems?
Cybersecurity requires continuous adaptation because attackers continually change their methods.
IronClad Defense Systems brings AI-driven analysis and behavioral intelligence into the security environment, helping organizations improve threat visibility and respond to suspicious activity more effectively.
Its AI-focused approach can support organizations looking to move beyond purely reactive security and toward a more adaptive, data-driven cybersecurity strategy.
Build a Smarter Security Posture With IronClad Defense Systems
The modern threat landscape demands security technologies capable of handling large volumes of information and adapting to changing attack patterns.
IronClad Defense Systems AI Security is designed to help organizations detect unusual behavior, analyze potential threats, strengthen endpoint protection, and support more intelligent access controls.
By combining AI-driven security with established cybersecurity practices, organizations can build a stronger and more resilient defense against evolving digital threats.
Stay Ahead With AI-Powered Cybersecurity
Threats will continue to evolve, but security strategies can evolve with them.
IronClad Defense Systems provides an AI-powered approach to cybersecurity that helps organizations turn security data into actionable intelligence, improve threat detection, and strengthen their overall digital defenses.